Technology rarely gives people the luxury of standing still. As businesses move from traditional systems to cloud platforms, connected infrastructure and increasingly complex digital environments, the people responsible for keeping those systems secure have had to evolve just as quickly. Cybersecurity is no longer limited to technical teams; it touches governance, risk, operations, business continuity and the people making decisions behind technology.
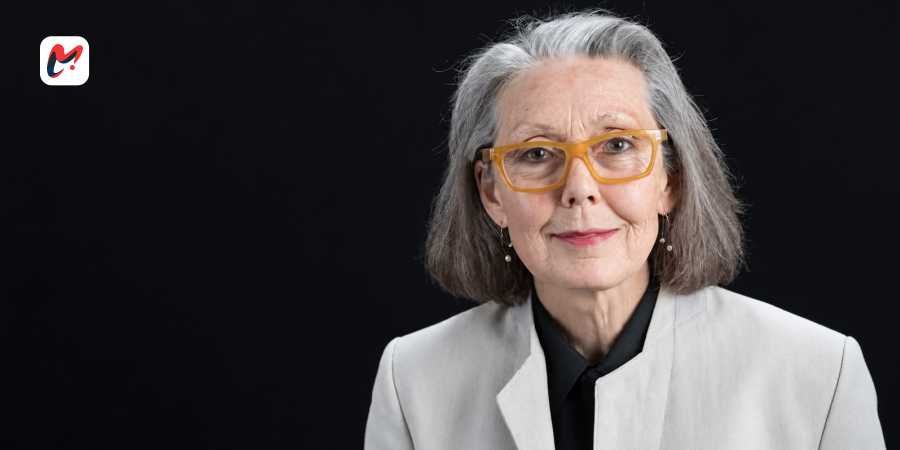
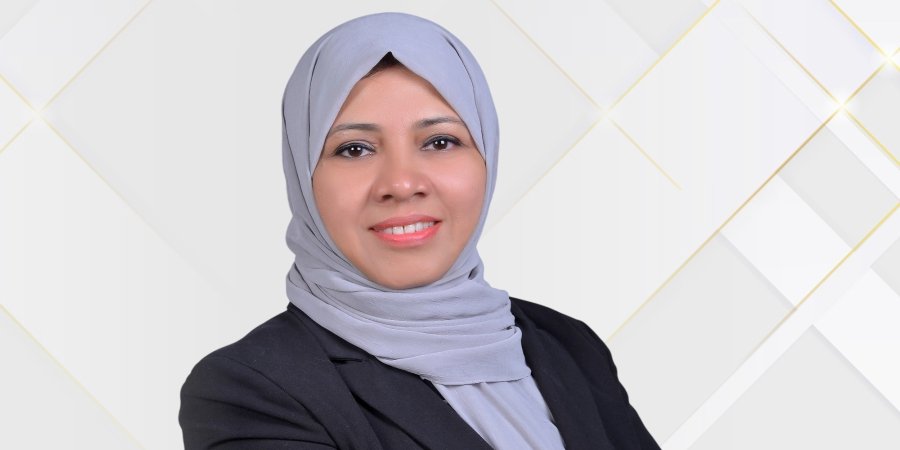
Within this changing landscape, Dr. Yasmin Razack, Lead Assessor and Trainer at Gabriel Registrar and a specialist in Cybersecurity Governance, Risk and Compliance (GRC) and ISO standards, has built a career spanning more than 25 years across IT, aviation and fintech. She has extensive experience establishing security infrastructure and driving compliance across major enterprises and government sectors. Her work includes helping establish Emirates Airline’s Network Operations Center (NOC), building high-availability defense frameworks, and translating complex regulatory requirements into practical enterprise risk strategies.
Cybersecurity was not her original destination. She began as a technical expert, drawn to solving problems and fixing things. Over time, her work moved toward processes, governance and risk, broadening her understanding of what security means to an organization.
A Turning Point in Her Career
Emirates Airline sponsored Yasmin for an MBA, a significant turning point that helped her move into leadership. She went on to establish a Network Operations Center for the airline from the ground up, developing its people, processes and operational foundations. The experience strengthened her appreciation of governance, risk and cybersecurity, while reinforcing the importance of developing others.
A Lean Six Sigma project at Emirates Airline prompted another shift and eventually led her toward a doctorate in cybersecurity assurance. Looking back, her career reflects less a carefully mapped route than a willingness to learn, take on unfamiliar challenges and recognize opportunities as they arise.
A Complex Cybersecurity Landscape
The Arab region’s ambitious digital and smart-city projects are expanding the attack surface. Cloud platforms, artificial intelligence (AI), the Internet of Things (IoT) and connected critical infrastructure create new governance and security challenges. Yasmin believes AI governance will be among the most pressing concerns. AI can strengthen organizations, but it can also give attackers new capabilities. Shadow AI and the use of public language models with corporate data can create exposure, making responsible AI use and stronger data protection essential.
Regulatory compliance is also becoming more complex as organizations operate across jurisdictions and rely more heavily on vendors and digital partners. Yasmin sees an opportunity for the UAE to play a leading role in building a secure and trusted digital economy.
A Broader View of Risk and Leadership
Experience across aviation, banking, finance, education and IT has shaped Yasmin’s leadership philosophy around adaptability, evidence and risk. Working in an airline employing people from more than 160 nationalities taught her that leadership cannot follow a single formula. Different industries and cultures bring different risks, regulations and expectations, requiring decisions that balance security with business and operational realities.
Her Lean Six Sigma background reinforces the value of data, evidence and root-cause analysis. She believes lasting change comes when people are empowered to take ownership and improve processes, rather than simply react to problems.
Making Innovation Secure by Design
Yasmin believes security should be built into innovation rather than added afterwards. Her approach rests on four practical principles: secure guardrails instead of excessive gatekeeping, a clearly defined risk appetite, continuous compliance and a no-blame security culture. Pre-approved infrastructure, change templates and embedded security controls can help teams move quickly without abandoning safeguards. Risk-based controls ensure low-risk initiatives are not unnecessarily restricted, while automated monitoring can identify issues faster than annual audits.
She also believes employees must feel comfortable reporting mistakes and vulnerabilities. A culture focused on learning and root causes is more effective than one built around blame.
Bridging Business and Technology
Her experience as a Change Management Head at Emirates Airline and Network International required Yasmin to connect executive concerns about business value and risk with technical teams’ focus on architecture and security. In aviation, cybersecurity had to support operational continuity, passenger safety, compliance and customer experience. In banking, decisions also had to account for customer trust, regulatory expectations and growth. Her role was to create a common language that helped business and technical teams make decisions about risk, investment and resilience together.
Developing the Next Generation
Yasmin’s commitment to developing cybersecurity talent comes from seeing what young professionals can achieve when given responsibility and guidance. At Emirates Airline, she coordinated mentorship for the Emirati internship programme and recruited five graduates into her NOC team. Within a year, one graduate developed the capability to manage critical mainframe operations traditionally handled by experienced staff.
Her work with MAHE University has continued this focus through initiatives exploring trainee security auditors and ISO lead-auditor training for postgraduate students. She believes future cybersecurity professionals need more than technical knowledge: curiosity, ethical judgment, adaptability, communication and business understanding are equally important.
Governing the Risks of Emerging Technology
Yasmin expects AI to have the most immediate impact on governance, bringing concerns around data provenance, model risk, privacy, third-party services and AI-enabled attacks. She also urges organizations to prepare for the quantum era by building cryptographic inventories, identifying vulnerable systems and planning a transition to post-quantum cryptography.
Blockchain can create opportunities in data integrity, digital identity and traceability, but it also brings risks involving smart contracts, key management and accountability. Emerging technologies, in her view, should be governed according to their actual business purpose and risk context. Technology governance is inseparable from business continuity, regulatory responsibility and customer trust.
The First Line of Defense Is Already at Work
Yasmin believes a strong security culture begins when employees are treated as part of the defense, not as the weakest link. Cybersecurity should be everyone’s responsibility, supported by continuous, role-specific learning rather than annual training alone.
Procurement teams can learn about supply-chain risks, developers about secure coding, finance teams about payment fraud, and other employees about phishing and social engineering. Real incidents should become learning opportunities, supported by a no-blame culture that encourages early reporting. She also advocates Cyber Champion networks, recognition for secure behavior, and practical metrics such as phishing-reporting rates and repeat incidents—not just training completion. Nominating a Cyber Champion in every department can help bridge cybersecurity and business teams.
Security should become part of onboarding, procurement, projects and supplier management. Leadership must connect security with customers, people, reputation and business continuity.
The Achievement That Matters Most
The achievement that gives Yasmin the greatest pride is the people she has helped develop. Several professionals she mentored have progressed into management and leadership roles across banking, telecommunications and IT.
She is also proud of establishing the NOC at Emirates Airline from the ground up, including its team, processes, policies and rosters, delivering a responsive 24/7 monitoring capability that safeguarded enterprise operations. Her doctoral research and co-authored book on blockchain applications provided aviation organizations with forward-looking blueprints for secure innovation. Her security posture assessments for major government and semi-government entities continue to provide leaders with actionable risk insights. She is also an advisory board member for the University of Fairfax in Virginia, USA.
Why She Kept Moving
Three principles have shaped Yasmin’s decisions throughout her career: adaptability, accountability and continuous improvement. She deliberately moved between departments roughly every three years to keep learning and avoid becoming tied to a single function or technology. During crises, she believes leaders must take responsibility and make difficult decisions.
Her Lean Six Sigma experience reinforced the importance of understanding root causes, using data and improving processes rather than simply reacting to problems. As technology changes, she continues to see learning, adaptability and people development as essential to effective leadership.
A Legacy Built Through People
Being recognized among the Arab World’s 20 Most Iconic Women Leaders to Watch is an honor Yasmin values, but she measures leadership by the opportunities created for others. Her ambition is to help people move beyond self-doubt and understand that cybersecurity leadership is not limited to those with deep technical expertise. Curiosity, adaptability and the willingness to keep learning can be equally valuable.
She believes human capability should remain at the center of cybersecurity. Her guiding principle is simple: do not make yourself indispensable. Build people who can do what you do, share knowledge and give them room to grow. If those people eventually become mentors and leaders themselves, Yasmin believes that will be the legacy worth leaving behind.